About Cipherstep
Financial systems make important decisions using information collected on a customer’s device. An attacker who controls the app or its runtime can interfere with that information before it reaches the bank’s backend. We built Cipherstep to protect this exposed part of the anti-fraud system.
Founded by security researchers
Cipherstep was founded by client security researchers. Our work focuses on the layer between a customer and a financial institution: the device and the running application that collect evidence, handle requests, and supply context for fraud decisions.
When a financial institution receives that information, the collection environment matters. A manipulated app can deliver plausible data through an otherwise legitimate flow. We question assumptions about that environment and build tools to examine what is happening inside it.
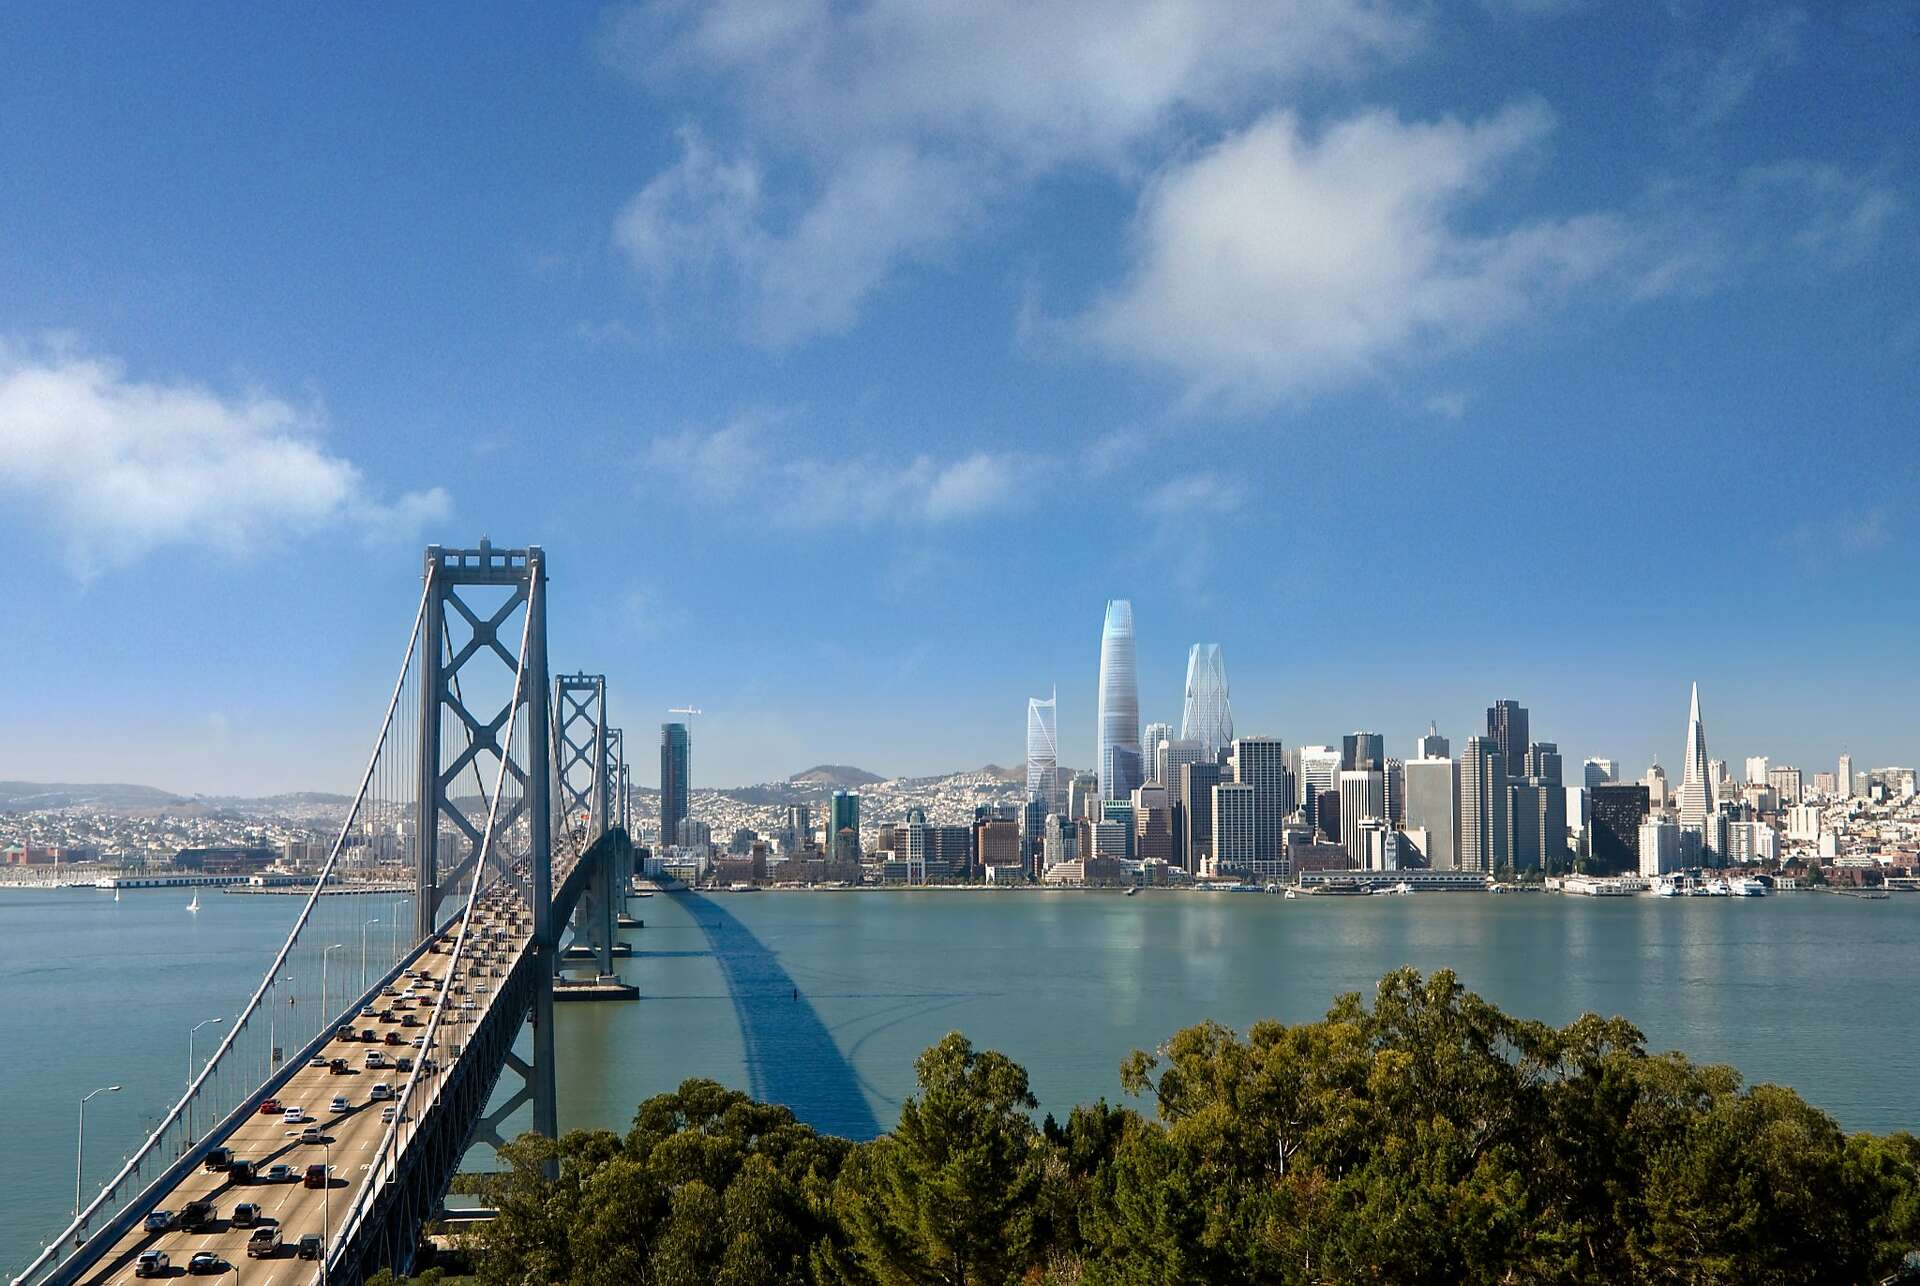
Based in San Francisco
We’re based in San Francisco, a city where software is built, broken, and rebuilt every day. Working at the center of software innovation keeps us close to the questions shaping finance and automation. It is a fitting place to build defenses for the systems those changes depend on.
Protecting the integrity layer
Our mission is to protect device and runtime integrity for banking and finance, where client compromise can have serious consequences for businesses and the people they serve. Account opening, access, and money movement all depend on evidence arriving from environments outside the institution’s direct control.
Cipherstep collects supported client observations and seals its evidence for server-side analysis. Runtime protection can interrupt supported manipulation inside the app. Together, these give financial teams more context for their decisions while identity, authentication, and transaction controls continue to do their own work.
Research that keeps moving
Our approach is grounded in research. We investigate operating-system and firmware behavior, question security assumptions, and test our findings against supported environments. Understanding how a system actually behaves takes careful work, especially when someone is trying to conceal what they have changed.
Attackers study defenses and adapt their techniques. Operating systems change, and yesterday’s assumptions need to be examined again. Staying on the bleeding edge means continuing that specialist work: developing anti-analysis techniques, testing new observations, and revisiting the limits of our detections as the environment evolves.
A future built on trusted interactions
Our long-term vision is an online financial system where businesses can trust both human actors and verified personal agents acting with their authorization. We want the integrity of the collection and execution environment to become part of that foundation, alongside identity, authorization, and transaction controls.
A secured integrity layer would give businesses a stronger basis for deciding which interactions to accept and how much responsibility to delegate. Identity and authorization still determine who—or what—is permitted to act; integrity helps assess the environment carrying out that action. That is the future we are working toward.